EU Cyber Resilience Act (CRA)

Preparing Connected Products for New Cybersecurity Requirements

The EU Cyber Resilience Act establishes cybersecurity requirements for products with digital elements sold in the European Union. It requires manufacturers to address cybersecurity throughout the product lifecycle, from product design and secure updates to vulnerability handling, incident reporting and long-term support.

Reporting obligations begin September 11, 2026. The main CRA requirements apply beginning December 11, 2027.

As manufacturers evaluate how their products will meet CRA requirements, cybersecurity, resilience, recovery and persistent-state retention become increasingly important design considerations.

Using our MRAM helps system designers address requirements commonly associated with cyber-resilient products by protecting critical data at the hardware level. MRAM natively supports security-by-design architectures, eliminates reliance on vulnerable external batteries, and enables ultra-fast firmware rollback and recovery mechanisms designed to preserve trusted operation during faults, interruptions and active exploits.

While our MRAM is not itself a CRA certification solution, it helps simplify implementation of capabilities customers may need to address in products being developed for CRA-regulated markets.

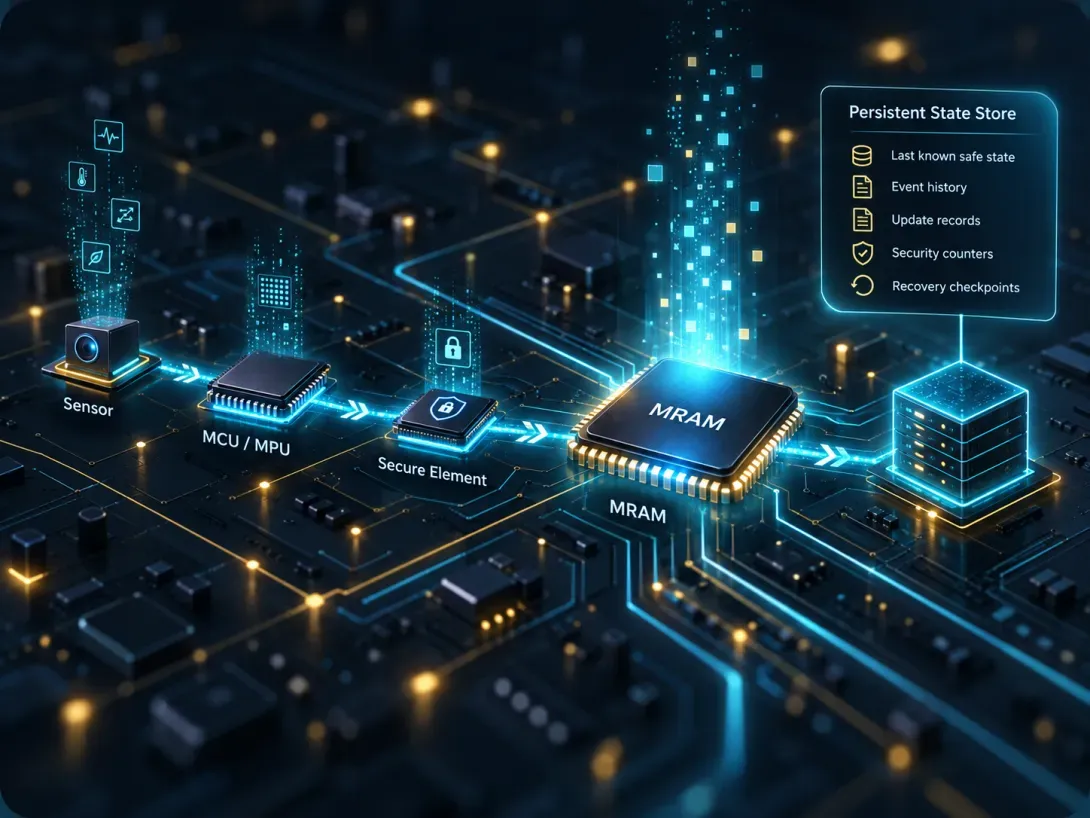
Persistent State MRAM Pipeline

Where Memory Meets CRA

The Cyber Resilience Act places increased emphasis on secure updates, vulnerability management, event records, system recovery and maintaining products throughout their lifecycle.

Meeting these objectives depends on information that remains available before, during and after interruptions. Firmware status, recovery checkpoints, event logs, configuration settings and operational state all help support trusted operation and system recovery.

We call this Persistent Safety State.
teal icon representing white papers

Advantages of using Everspin Technologies MRAM for EU Cyber Resilience Act related security goals

Download White Paper
teal icon representing factsheet and requirements

Cyber Resilience Act (CRA) Requirements

Explore
teal blog icon

What Manufacturers Need to Know and Where MRAM Helps

Read Blog
teal contact us icon

Talk to an Expert

Contact Us

MRAM natively supports security-by-design architectures, eliminates reliance on vulnerable external batteries, and enables ultra-fast firmware rollback and recovery mechanisms designed to preserve trusted operation during faults, interruptions and active exploits.


These capabilities help support:

  • Persistent operational state retention
  • Secure firmware rollback architectures
  • High-endurance event logging
  • Recovery checkpoint preservation
  • Battery-free retention of critical data
  • Persistent Safety State